Rating
Innovation
Pricing
Technology
Usability
We have discovered similar tools to what you are looking for. Check out our suggestions for similar AI tools.
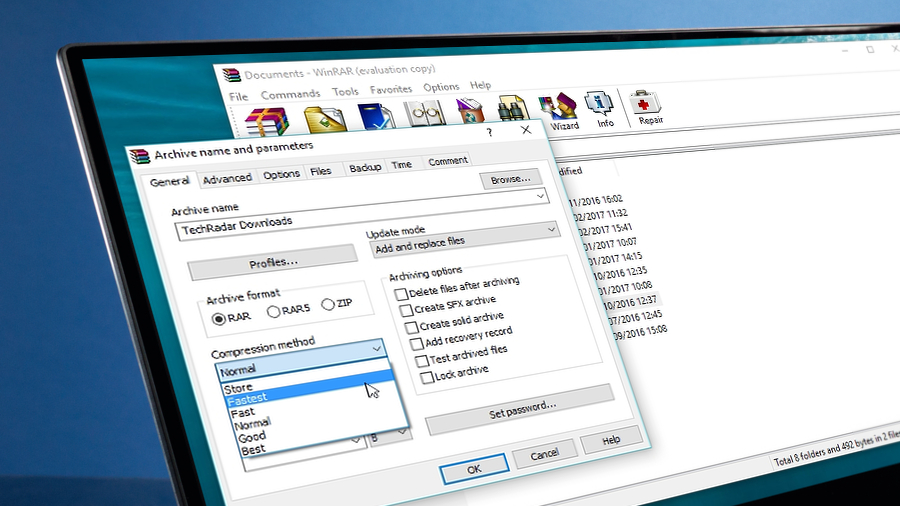
Two Russian APT groups are exploiting a WinRAR flaw patched nearly a year ago to hit Ukraine
Two Russian state-linked hacking groups are actively exploiting a path traversal vulnerability in WinRAR that was patched nearly a year ago, using it to deploy credential-stealing malware against Ukra [...]
Mythos autonomously exploited vulnerabilities that survived 27 years of human review. Security teams need a new detection playbook
A 27-year-old bug sat inside OpenBSD’s TCP stack while auditors reviewed the code, fuzzers ran against it, and the operating system earned its reputation as one of the most security-hardened platfor [...]
200,000 MCP servers expose a command execution flaw that Anthropic calls a feature
Anthropic created the Model Context Protocol as the open standard for AI agent-to-tool communication. OpenAI adopted it in March 2025. Google DeepMind followed. Anthropic donated MCP to the Linux Foun [...]
Anthropic and OpenAI just exposed SAST's structural blind spot with free tools
OpenAI launched Codex Security on March 6, entering the application security market that Anthropic had disrupted 14 days earlier with Claude Code Security. Both scanners use LLM reasoning instead of p [...]
Running Claude Code or Claude in Chrome? Here's the audit matrix for every blind spot your security stack misses
Between May 6 and 7, four security research teams published findings about Anthropic’s Claude that most outlets covered as three separate stories. One involved a water utility in Mexico, another tar [...]
7,000 Langflow servers are under attack. LangGraph and LangChain have the same holes
Your AI agent did exactly what it was designed to do. The framework underneath it just handed an attacker a shell on the box that holds your OpenAI key, your database credentials, and your CRM tokens. [...]
Anthropic's Claude Code Security is available now after finding 500+ vulnerabilities: how security leaders should respond
Anthropic pointed its most advanced AI model, Claude Opus 4.6, at production open-source codebases and found a plethora of security holes: more than 500 high-severity vulnerabilities that had survived [...]
The Shai-Hulud npm worm didn't fake its security check — it earned a legitimate one
An attacker on Tuesday took over the GitHub account of the developer who maintains keyv, a small key-value storage library that npm serves roughly 127 million times a week. Within hours, poisoned vers [...]